
N2SF & Zero Trust Transition Consulting
Design a security transition around your information.
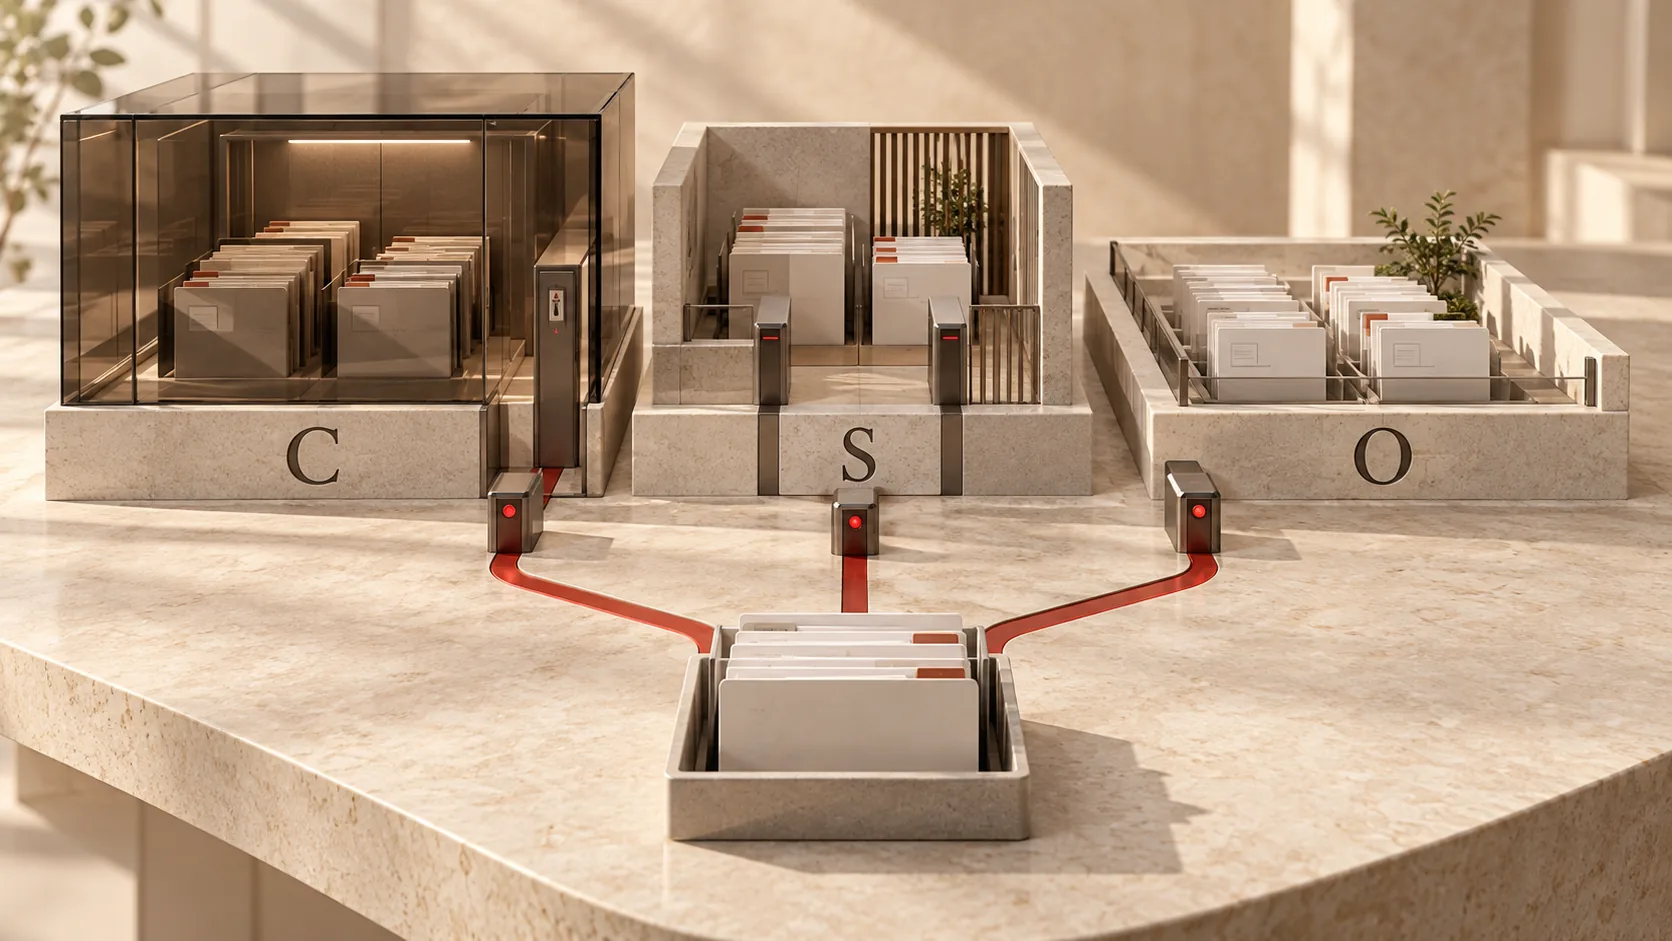
From classification to daily operations.
For national and public institutions adopting Korea’s National Network Security Framework (N2SF), we review information and systems, define classification criteria and security measures, and plan implementation.
N2SF addresses information protection needs and processing environments. Zero Trust develops controls for access to resources. We connect these perspectives in a transition plan suited to the institution’s work and operating conditions.
Connect information protection needs with access controls.
C Classified
Review significance and handling requirements
S Sensitive
Define permitted use and protection measures
O Open
Review disclosure scope and conditions for use
Scope of services
Discovery & transition scope
Review work, information, system inventories and network layouts against applicable requirements to establish scope and priorities.
- Review work and asset inventories
- Identify transition and retained protection areas
- Assess tasks and resource needs
Information classification
Connect information to business functions, record C/S/O classification criteria and evidence, and define verification, approval and change processes.
- Identify information by business function
- Record classification decisions and evidence
- Define review, approval and reclassification
Controls & review documentation
Assess processing environments and threats, identify security controls and implementation tasks, and support security review documentation.
- Review service models and threats
- Map controls and implementation tasks
- Prepare supporting review documents
Zero Trust & implementation roadmap
Review access controls and operational capabilities to set targets and plan phased tasks, transition exceptions and review procedures.
- Review capabilities and target maturity
- Prioritize phased implementation tasks
- Define transition exception management
Who this engagement can support
- Institutions defining which network areas retain separation and which may transition
- Teams setting rules and approval procedures for generative AI use
- Institutions preparing information classifications and security review documents
- Teams defining transition scope, priorities and budget assumptions
Document decisions and make the plan actionable.
- Information classification register
- Decision evidence and review records
- Security control mapping
- Phased implementation roadmap
- Security review supporting documents
Deliverables and engagement scope are agreed according to institutional requirements and project scope.
N2SF adoption preparation checklist
Explore 15 questions and records to prepare across five areas to support your institution’s transition planning.
Engagement process
01
Discover & scope
Review work, systems and applicable requirements to define scope and priorities.
02
Classify & design
Assess information and processing environments, then document classifications, controls and review evidence.
03
Plan implementation
Define implementation tasks, transition management and follow-up review arrangements.
Frequently asked questions
Does N2SF mean opening every network?
It means designing protection measures for information classifications, environments and applicable requirements. We review where separation or blocking is needed alongside permitted uses.
Can the engagement cover AI use?
We review information permitted for external AI services, protective measures and internal approval procedures in the relevant classification and service environment.
What follows initial classification?
Maintain decision evidence as work, information and systems change, with procedures for access control, exceptions and implementation tracking.
The scope of work and deliverables are determined by the target environment and the agreed engagement.
Start with a scope that fits your institution.
Discuss the support needed for your environment and current preparations.